Strengthening cybersecurity in an increasingly digital banking environment
As financial institutions accelerate their digital transformation, cybersecurity has become one of the most critical foundations of trust, operational resilience, and business continuity.
Banks today operate within increasingly complex technology environments. Digital banking platforms, payment infrastructure, enterprise applications, cloud services, and interconnected networks enable institutions to serve customers more efficiently and introduce innovative financial products. However, this growing digital footprint also creates new security challenges.
Financial institutions must continuously monitor their technology environments, identify suspicious activity, investigate potential threats, and respond effectively to cybersecurity incidents. Protecting sensitive financial information and maintaining the availability of critical banking services requires more than deploying individual security tools. It demands a coordinated approach that brings together people, processes, technology, and operational intelligence.
At Access 89, we believe effective cybersecurity begins with building the right operational foundations.
This philosophy guided our engagement with CalBank PLC, one of Ghana’s established financial institutions, where Access 89 was entrusted with establishing the bank’s Security Operations Center (SOC) from the ground up.
The project brought together our expertise in cybersecurity architecture, security systems integration, operational processes, and enterprise technology implementation to establish a centralized capability for monitoring and responding to security threats. Our work focused not simply on deploying cybersecurity technology, but on helping create the operational structure required to support continuous security monitoring, incident investigation, and coordinated response.
The challenge: moving toward centralized security operations
Modern banking environments generate enormous volumes of security-relevant information. Activity across servers, applications, databases, networks, endpoints, and security infrastructure can provide important indicators of potential threats.
However, the ability to collect security information does not automatically translate into the ability to identify and respond to cyber incidents effectively. Security events must be brought together, analyzed, prioritized, and investigated within a structured operational environment.
Without centralized visibility, security teams may face challenges identifying relationships between events occurring across different systems. An isolated authentication failure, an unusual network connection, or an unexpected administrative activity may appear insignificant on its own. When analyzed together, however, these events can provide important indications of suspicious behavior.
For financial institutions, the consequences of delayed detection or ineffective incident coordination can be significant. Security incidents may affect the confidentiality of customer information, the integrity of financial systems, the availability of digital services, and the institution’s overall operational resilience.
Establishing a Security Operations Center provides a structured way to address these challenges. For CalBank, the engagement with Access 89 centered on developing this capability as an integrated security function rather than a collection of disconnected security products.
The objective was to establish a foundation through which security events could be monitored, potential threats investigated, and incident response activities coordinated more effectively.
Building the Security Operations Center from the ground up
Establishing a Security Operations Center is a complex undertaking. It requires much more than installing monitoring software or creating dashboards. An effective SOC combines security architecture, technology integrations, operational procedures, skilled personnel, and clearly defined responsibilities.
Access 89 approached the CalBank engagement as an end-to-end security operations implementation. Our work involved developing the technical and operational foundations needed to establish a centralized security monitoring environment. The engagement brought together several essential components of modern security operations.
Establishing the security architecture
A Security Operations Center must be designed around the technology environment it is intended to protect. This requires understanding the systems, applications, infrastructure, and security controls that generate relevant security information. The architecture must also support the secure collection, processing, analysis, and retention of security events.
Access 89’s work focused on establishing a security operations architecture capable of bringing relevant information into a centralized monitoring environment. This provided the foundation for connecting security technologies and supporting structured threat detection and investigation.
Centralizing security monitoring
One of the core objectives of a SOC is to provide security teams with a consolidated view of activity across the technology environment. By integrating relevant security data sources into a centralized monitoring capability, analysts can examine events from multiple systems and identify patterns that may require investigation.
This approach supports better visibility into potential security incidents and reduces dependence on reviewing individual systems in isolation. Centralized monitoring also creates opportunities to correlate related events, prioritize alerts, and support more consistent investigation procedures.
Enabling threat detection and investigation
Detecting cybersecurity threats requires the ability to distinguish potentially malicious activity from routine system behavior. A SOC must therefore support the analysis of security events, identification of suspicious patterns, and investigation of alerts.
Access 89’s implementation established the technical foundation for structured security monitoring and threat investigation. This included supporting the processes through which security events could be reviewed, assessed, and escalated when necessary. By creating a centralized operational capability, the bank gained a stronger foundation for identifying potential threats and coordinating security investigations.
Establishing incident response processes
Security monitoring is only effective when organizations can respond appropriately to the threats they identify. A Security Operations Center must therefore operate within a defined incident management framework. This includes procedures for classifying security events, determining incident severity, escalating issues, coordinating investigations, and documenting response activities.
As part of establishing the SOC, Access 89 focused on the operational processes needed to support consistent security incident management. These processes help ensure that potential threats can be handled through structured procedures rather than relying entirely on ad hoc responses.
Supporting security governance and operational accountability
Cybersecurity operations require clear responsibilities and effective governance. Security teams need to understand how incidents are reported, who is responsible for investigations, when escalation is required, and how security activities are documented.
The establishment of the SOC provided an opportunity to formalize these operational responsibilities within a centralized security function. This creates a foundation for more consistent security oversight, management reporting, and continuous improvement.
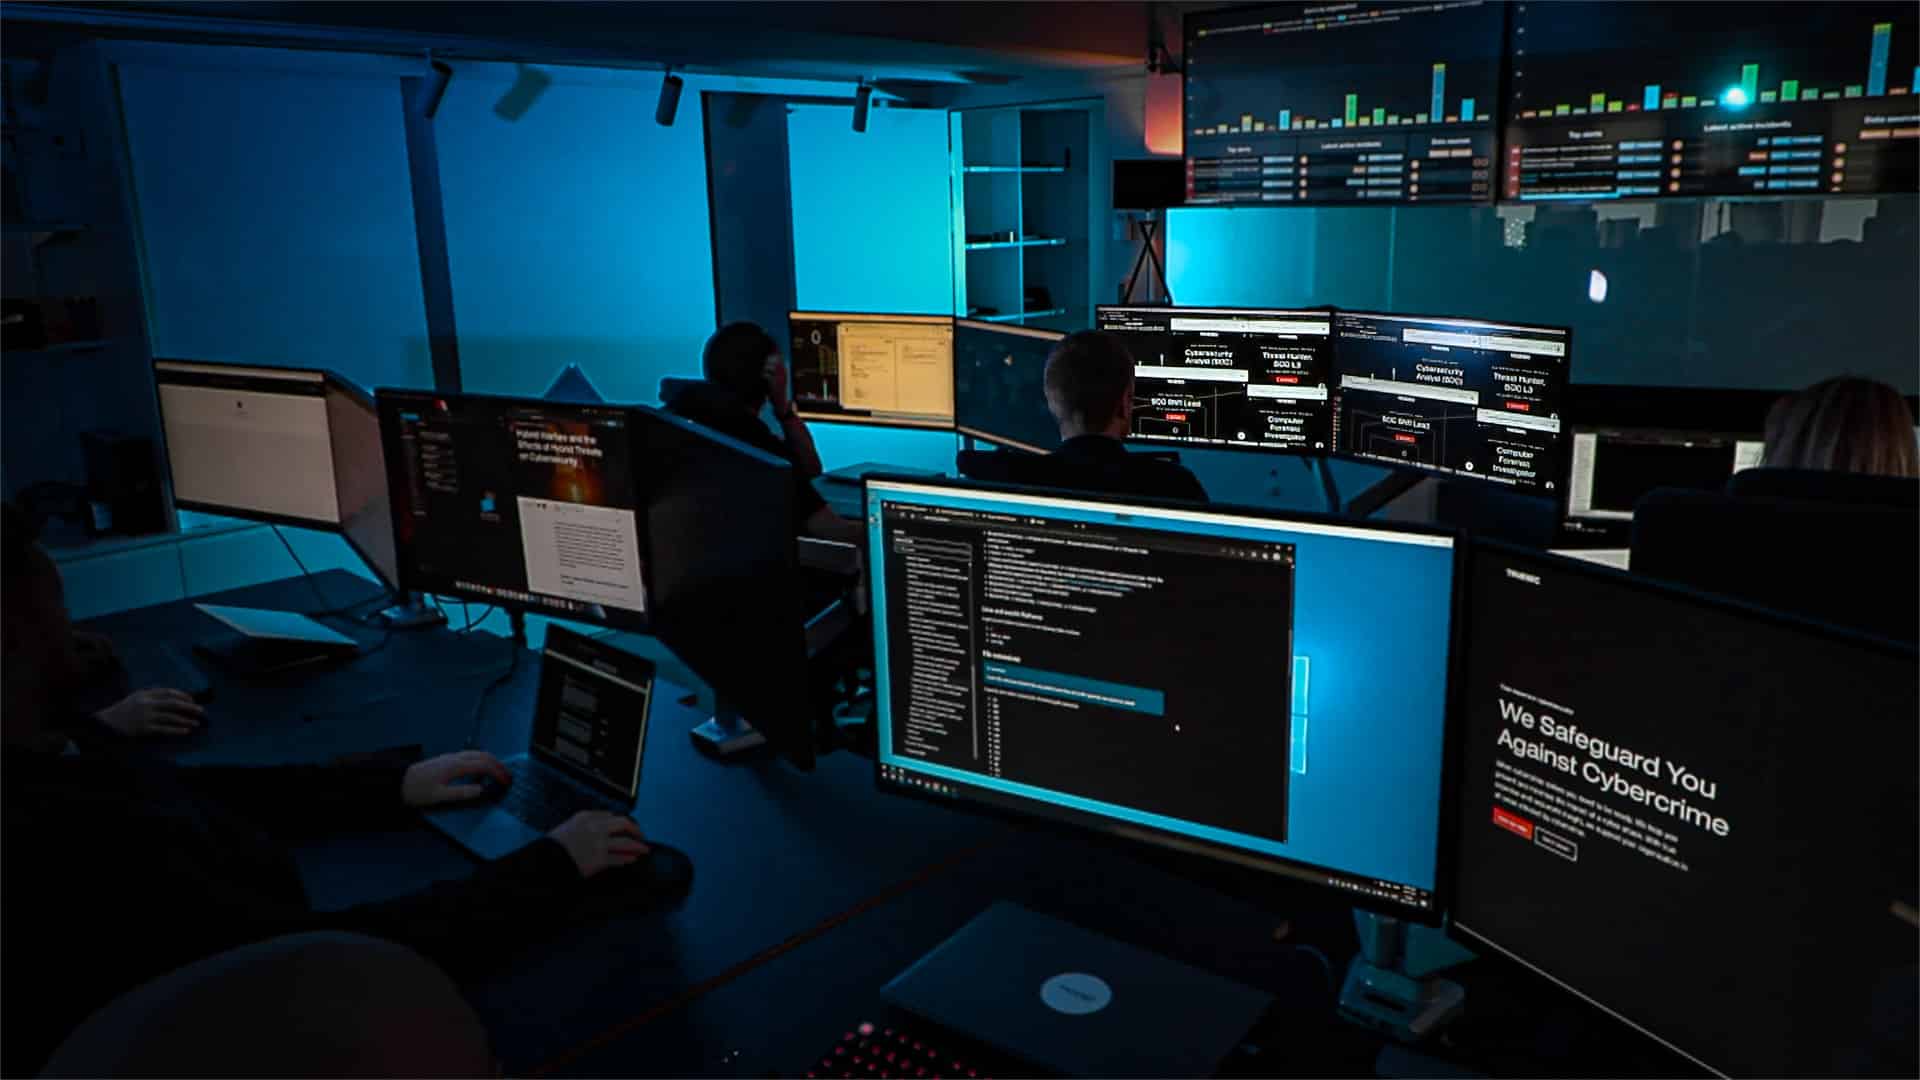
Our work focused not simply on deploying cybersecurity technology, but on helping create the operational structure required to support continuous security monitoring, incident investigation, and coordinated response.
From security tools to an operational security capability
One of the most important distinctions in the CalBank engagement was the focus on establishing an operational capability rather than simply implementing technology. Cybersecurity platforms can generate alerts, collect logs, and identify suspicious activities. However, these capabilities only create meaningful value when supported by the right operational processes.
Security analysts must be able to interpret alerts, investigate incidents, understand their potential impact, and coordinate appropriate responses. Management teams must also have visibility into security risks and the effectiveness of security operations.
Access 89’s approach recognized that the success of a Security Operations Center depends on the relationship between technology, processes, and people. The implementation was therefore designed to provide a structured foundation for security operations within the bank.
This approach supports the transition from fragmented security monitoring toward a more coordinated model of cybersecurity management. It also establishes the basis for continued improvements in threat detection, incident response, security analytics, and operational maturity.
Strengthening visibility across the banking technology environment
Visibility is a fundamental requirement for effective cybersecurity. Banks depend on numerous interconnected systems to deliver financial services. These systems generate information that can help security teams identify unusual activity, investigate potential compromises, and understand emerging threats.
A centralized Security Operations Center provides an environment where relevant security information can be collected and analyzed more consistently. For CalBank, the SOC implementation was designed to strengthen the bank’s ability to monitor its technology environment through a coordinated security function.
This approach helps security teams move beyond isolated monitoring activities toward a broader understanding of security events. By correlating information across relevant systems, analysts can investigate suspicious activities with greater context.
Centralized visibility also supports more structured security reporting and provides a foundation for evaluating security trends over time. For a financial institution, these capabilities are important components of maintaining operational resilience and protecting critical technology services.
Building a foundation for faster, more coordinated incident response
Cybersecurity threats can develop quickly. When suspicious activity is detected, the effectiveness of an organization’s response depends on its ability to assess the situation, determine the potential impact, and coordinate appropriate actions.
A Security Operations Center helps bring structure to this process. Rather than treating every alert as an isolated technical issue, security events can be evaluated through defined investigation and escalation procedures. The SOC established for CalBank provides a foundation for more coordinated security incident handling.
By bringing monitoring, investigation, and response processes into a centralized operational model, the bank is better positioned to manage potential security events consistently. This is particularly important in banking, where the timely investigation of threats can help reduce exposure to operational disruption and other cybersecurity risks.
The implementation also creates opportunities to strengthen incident response capabilities over time through improved procedures, additional integrations, and greater automation.
Supporting regulatory readiness and cybersecurity governance
Financial institutions operate within demanding regulatory and risk management environments. In Ghana, banks must consider cybersecurity and operational resilience requirements established by the Bank of Ghana, alongside applicable data protection obligations and internal governance standards.
A Security Operations Center is an important component of a broader institutional cybersecurity framework. It supports the monitoring, investigation, documentation, and reporting activities needed for effective security oversight.
Through the CalBank engagement, Access 89 helped establish a security operations capability that can contribute to the bank’s broader cybersecurity governance and risk management objectives. Centralized monitoring and documented incident management processes can also provide valuable operational evidence for internal reviews, risk assessments, and compliance activities.
While technology alone cannot guarantee regulatory compliance, a well-structured SOC helps provide the operational capabilities necessary to support a mature cybersecurity program.
Engineering security for long-term resilience
Cybersecurity is not a one-time implementation. Threats evolve, technology environments change, and organizations continually introduce new systems and digital services. A Security Operations Center must therefore be capable of adapting to new risks and operational requirements.
The work undertaken by Access 89 for CalBank established a foundation on which the bank can continue developing its security operations capabilities. As cybersecurity requirements evolve, this foundation can support additional monitoring integrations, refined detection capabilities, improved incident response procedures, and more advanced security analytics.
It also creates opportunities to introduce greater automation into repetitive security processes, helping analysts focus their attention on activities requiring deeper investigation.
The long-term value of a SOC lies in its ability to evolve alongside the organization it protects. By establishing the underlying technical and operational structure, Access 89 contributed to CalBank’s capacity to strengthen its cybersecurity posture over time.
Demonstrating Access 89’s enterprise cybersecurity capabilities
The CalBank engagement reflects an important part of Access 89’s broader engineering expertise. Our work extends beyond application development into the design and implementation of enterprise technology infrastructure that supports critical business operations.
Establishing a Security Operations Center for a financial institution requires an understanding of cybersecurity architecture, systems integration, operational processes, and the demands of highly regulated environments. It also requires the ability to translate complex security requirements into practical, functioning technology solutions.
Through this engagement, Access 89 demonstrated its capability to undertake complex cybersecurity implementation projects within the financial services sector. The project illustrates our approach to enterprise technology delivery: understanding the operational requirements, designing the appropriate architecture, integrating the necessary systems, and establishing the foundation for long-term value.
These same principles guide our work across software engineering, cloud infrastructure, digital financial services, enterprise integration, and managed technology services.
For organizations undergoing digital transformation, cybersecurity must be considered an essential component of their technology strategy rather than an afterthought. Our work with CalBank demonstrates how Access 89 helps organizations build the security foundations required to support that transformation.
Helping secure the future of digital banking
The future of banking will be increasingly digital, interconnected, and data-driven. As financial institutions expand their digital services, cybersecurity will remain fundamental to protecting customers, maintaining operational continuity, and sustaining trust.
Security Operations Centers play an important role in this environment by providing centralized capabilities for monitoring threats, investigating incidents, and coordinating responses. Through our work with CalBank PLC, Access 89 contributed to establishing this critical security capability from the ground up.
The engagement demonstrates how strategic cybersecurity engineering can help financial institutions strengthen their operational foundations and prepare for an increasingly complex threat landscape. For Access 89, it reinforces our commitment to helping African enterprises build secure, resilient, and scalable digital infrastructure.
Because building the future of digital banking isn’t only about creating new financial services. It’s also about engineering the security infrastructure that protects them.
- Cybersecurity
- Security Operations Center
- SOC
- Banking
- Incident Response
- Threat Detection
- Ghana
- Access 89
About Access 89
Access 89 is a technology and digital transformation company helping organizations design, engineer, secure, and operate modern digital infrastructure. Our expertise spans enterprise software engineering, cybersecurity, cloud infrastructure, systems integration, data and artificial intelligence, financial technology, and managed technology services. We work with organizations across industries to solve complex technology challenges, strengthen operational resilience, and build platforms that support long-term growth.